White House Gemini Chatbot Launch Sparks New AI Hallucination Risk Government Concerns
The White House's deployment of a Gemini-powered citizen chatbot has ignited debates regarding AI hallucination risk in government services. This development underscores the urgent need for new oversight frameworks to manage public-facing AI deployments effectively.
Published by
APEX AI Guardrails Editorial Team
October 3, 2026
Reading time
6
minutes
The recent launch of a Gemini-powered chatbot for citizen services by the White House has elevated concerns regarding AI hallucination risk government and the accountability of public-facing automated systems. While intended to streamline information delivery, the system lacks external oversight, creating significant liability concerns for federal administrators. For government IT and compliance leaders, this launch demonstrates that technological adoption is currently outpacing the development of robust, enforceable safety guardrails.
How does the White House’s new chatbot deployment impact AI hallucination risk government?
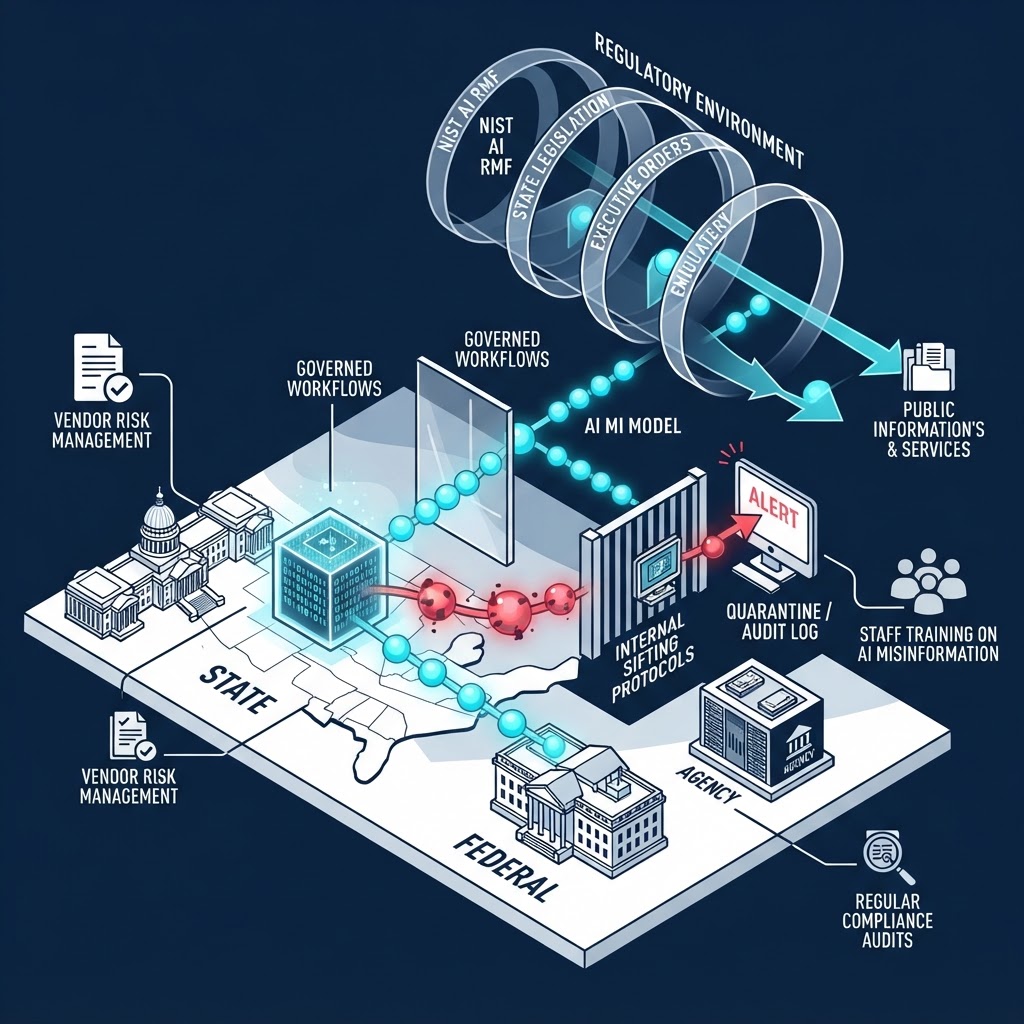
The deployment introduces potential for AI hallucination risk government by relying on generative models for public service delivery without independent oversight. This creates a liability gap, as federal agencies struggle to apply existing governance frameworks—such as those suggested by the NIST AI RMF—to unpredictable multimodal output. The lack of external validation mechanisms increases the likelihood of providing citizens with inaccurate or misleading information during critical interactions.
Legislative Waves and Regulatory Pressure in AI Governance
California Governor Gavin Newsom recently concluded his bill-signing period on September 30, 2026, enacting a dozen new AI-related measures that set a precedent for state-level accountability. These legislative actions reflect a growing trend toward formalizing expectations for AI safety and transparency, directly influencing how federal agencies approach their own AI governance charters. As noted in recent AI Governance News, the lack of standardized external oversight for tools like the new White House chatbot is at odds with the tightening regulatory environment emerging from state capitals.
Legislative bodies are increasingly demanding that public entities justify their reliance on black-box systems, particularly when those systems interface directly with the electorate. For agencies, this indicates that the era of pilot programs operating in a regulatory vacuum is ending. The AI Office and emerging enforcement architectures are now shifting their focus toward requiring audit trails that track decision provenance.
Agencies must prepare for a future where 'governed workflows' replace experimental, unvalidated AI deployments, aligning with the broader push for responsible AI and algorithmic accountability in the public sector.
What steps should agencies take to mitigate AI hallucination risk government during deployment?
Agencies should first move away from relying solely on human-in-the-loop verification and instead embed AI within governed workflows. This requires integrating continuous monitoring tools that align with OMB memoranda and NIST AI RMF guidelines. By automating the validation of AI outputs through internal sifting methods, agencies can extend existing control environments to their AI systems, ensuring that accountability remains firmly with the agency rather than the vendor.
Managing Operational Liability and Model Accountability
Federal agencies are facing a critical inflection point where AI hallucination risk government is no longer just a technical hurdle but a core legal and operational liability. As federalnewsnetwork.com explains, the solution lies in embedding AI systems directly into governed workflows to extend existing agency controls. Relying on the output of large language models without a structured risk management architecture exposes the government to misinformation that can undermine public trust and breach compliance protocols.
The challenge is magnified by the multimodal nature of modern tools, which can inadvertently generate hallucinated data that is difficult for traditional DLP software to detect. To manage this, leaders are looking toward new on-policy paradigms such as IRIS, which utilizes continuous implicit rewards to sift through outputs. This approach allows agencies to mitigate multimodal hallucinations without the prohibitive cost of relying exclusively on human or external evaluators.
By adopting these internal sifting mechanisms, agencies can better align their AI operations with the transparency mandates now being demanded by both the executive branch and state-level legislative leaders.
Navigating AI Integration for State and Municipal Entities
For state and local governments, the current environment necessitates a rapid re-evaluation of procurement and vendor risk management. The shift toward higher accountability standards means that public entities must move beyond basic SLAs and demand proof of model reliability and safety testing from their technology partners. When implementing AI for public service or internal workflow automation, municipal leaders should prioritize tools that allow for localized governance and granular output controls.
There is a pressing need to update agency AI acceptable use policies to reflect the dangers of relying on unvetted AI, particularly for citizen-facing communications. Furthermore, staff training must evolve to help employees identify the signs of AI-generated misinformation before it is distributed. The procurement process should now feature strict requirements for algorithmic transparency, ensuring that any AI tool integrated into a government workflow is subjected to rigorous, repeatable testing.
By establishing these boundaries, local entities can mitigate the risks associated with rapid adoption while fostering a culture of responsible AI. This proactive approach ensures that innovation does not come at the cost of public trust or institutional compliance, ultimately protecting the agency from the evolving liabilities inherent in modern AI deployments.
Strategic Mandates for Government IT Leadership
- →Establish internal sifting protocols to detect and flag AI-generated hallucinations before information reaches the public. • Review current AI acceptable use policies to ensure they specifically address the liabilities of generative model deployments. • Shift procurement strategies to mandate transparency documentation that aligns with the NIST AI RMF. • Prioritize the integration of on-policy reward-guided frameworks to automate risk mitigation in real-time. • Conduct regular audits of public-facing AI tools to verify output accuracy and maintain compliance with emerging state and federal mandates. • Require vendors to provide clear, actionable evidence of model safety and external verification capabilities during the RFP process.
What are the primary consequences of failing to address AI hallucination risk government?
Failure to address AI hallucination risk government can lead to severe reputational damage, loss of public trust, and significant legal liability if agencies provide inaccurate guidance on public services. Beyond immediate compliance failures, such errors can prompt intervention from regulatory bodies, resulting in forced system shutdowns and the imposition of rigid, costly oversight architectures that stifle future innovation and agency efficiency.
Tagged
About APEX AI Guardrails: We publish expert AI news and governance insights updated 4× daily. Our editorial team consists of retired government IT professionals, AI governance specialists, and compliance experts with deep experience in local government operations.